CMMC Level 1
CMMC Level 1 Has 15 Requirements, Not 17 Controls
Why you see 15, 17, 49, and 61 for CMMC Level 1, and the correct answer. Fifteen requirements, fifty-nine objectives, six domains, and no numeric score.
Search for the size of CMMC Level 1 and you get four different answers. Some pages say 15 requirements, others say 17 controls, and forum threads throw around 49 or 61 objectives. When guides, MSPs, and even other vendors disagree on the count, it is hard to trust anything else they say. Here is the correct answer, where the other numbers come from, and the rule text that settles it.
The short version. CMMC Level 1 has 15 security requirements, broken into 59 assessment objectives, across 6 domains. The 15 are the basic safeguarding items in FAR 52.204-21(b)(1), lettered i through xv, which 32 CFR 170.14(c)(2) adopts as Level 1. Level 1 exists to protect Federal Contract Information. It has no numeric score and no Plan of Action and Milestones. A page that says 17 is counting the NIST SP 800-171 mapping or quoting a superseded DoD guide.
Why the Confusion Exists
The number 17 has two real sources, and neither one changes the count.
- The NIST mapping, which is current. The CMMC rule maps each Level 1 requirement to NIST SP 800-171A (June 2018). One requirement, PE.L1-b.1.ix, covers visitors, physical access logs, and physical access devices in a single FAR item. The mapping splits its three phrases across three NIST numbers, 3.10.3, 3.10.4, and 3.10.5. So 15 FAR items line up with 17 NIST numbers. Both describe the same protections.
- The December 2021 DoD guide, which is superseded. The CMMC Self-Assessment Guide, Level 1, Version 2.0, published in December 2021, organized Level 1 as 17 practices, with identifiers built from NIST numbers such as AC.L1-3.1.1. The current DoD CMMC Assessment Guide, Level 1, Version 2.13, published in September 2024, lists 15 requirements, with identifiers built from the FAR paragraph such as AC.L1-b.1.i.
So a page that says 17 is not inventing the number. It is counting the mapping, or it is working from a superseded source. The count that applies to Level 1 today is 15 requirements.
The word controls adds to the mix. FAR 52.204-21(b)(1) itself introduces its list as "security controls," and the CMMC rule calls the same items security requirements. We use the rule's term and count them as 15 requirements.
What the Current Authority Says
Three primary sources settle the count, and each one is public.
- FAR 52.204-21(b)(1). The clause lists the basic safeguarding items as paragraphs (i) through (xv). That is 15 items.
- 32 CFR 170.14(c)(2). The CMMC rule reads, "The security requirements in CMMC Level 1 are those set forth in 48 CFR 52.204-21(b)(1)(i) through (xv)."
- 32 CFR 170.15(c)(1)(ii), Table 2. The rule's mapping table lists the 15 Level 1 identifiers against NIST SP 800-171A (June 2018). The three phrases of PE.L1-b.1.ix map to 3.10.3, 3.10.4, and 3.10.5, and every other identifier maps to one NIST number. That is where 17 appears, as a mapping, not as a count.
The DoD CMMC Assessment Guide, Level 1, Version 2.13 agrees. Its introduction describes Level 1 as the 15 basic safeguarding requirements in FAR 52.204-21. If a DoD solicitation from 2026 shows FAR 52.240-93 instead, that is the same 15 items under the FAR overhaul class deviations. The CMMC rule still cites 52.204-21.
The 15 CMMC Level 1 Requirements
Here are the 15 requirements with their identifiers and a plain-English summary of each. Each identifier links to its own page, which shows the official text and its source.
- AC.L1-b.1.i, limit system access to authorized users
- AC.L1-b.1.ii, limit access to permitted transactions and functions
- AC.L1-b.1.iii, verify and control connections to external systems
- AC.L1-b.1.iv, control information posted to publicly accessible systems
- IA.L1-b.1.v, identify system users, processes, and devices
- IA.L1-b.1.vi, authenticate users before granting access
- MP.L1-b.1.vii, sanitize or destroy media before disposal or reuse
- PE.L1-b.1.viii, limit physical access to systems and equipment
- PE.L1-b.1.ix, escort visitors, log physical access, and manage physical access devices
- SC.L1-b.1.x, monitor and control communications at the boundary
- SC.L1-b.1.xi, separate publicly accessible systems from internal networks
- SI.L1-b.1.xii, identify, report, and correct system flaws
- SI.L1-b.1.xiii, protect against malicious code
- SI.L1-b.1.xiv, keep malicious code protection current
- SI.L1-b.1.xv, perform periodic and real-time scans
The 59 Objectives Across 6 Domains
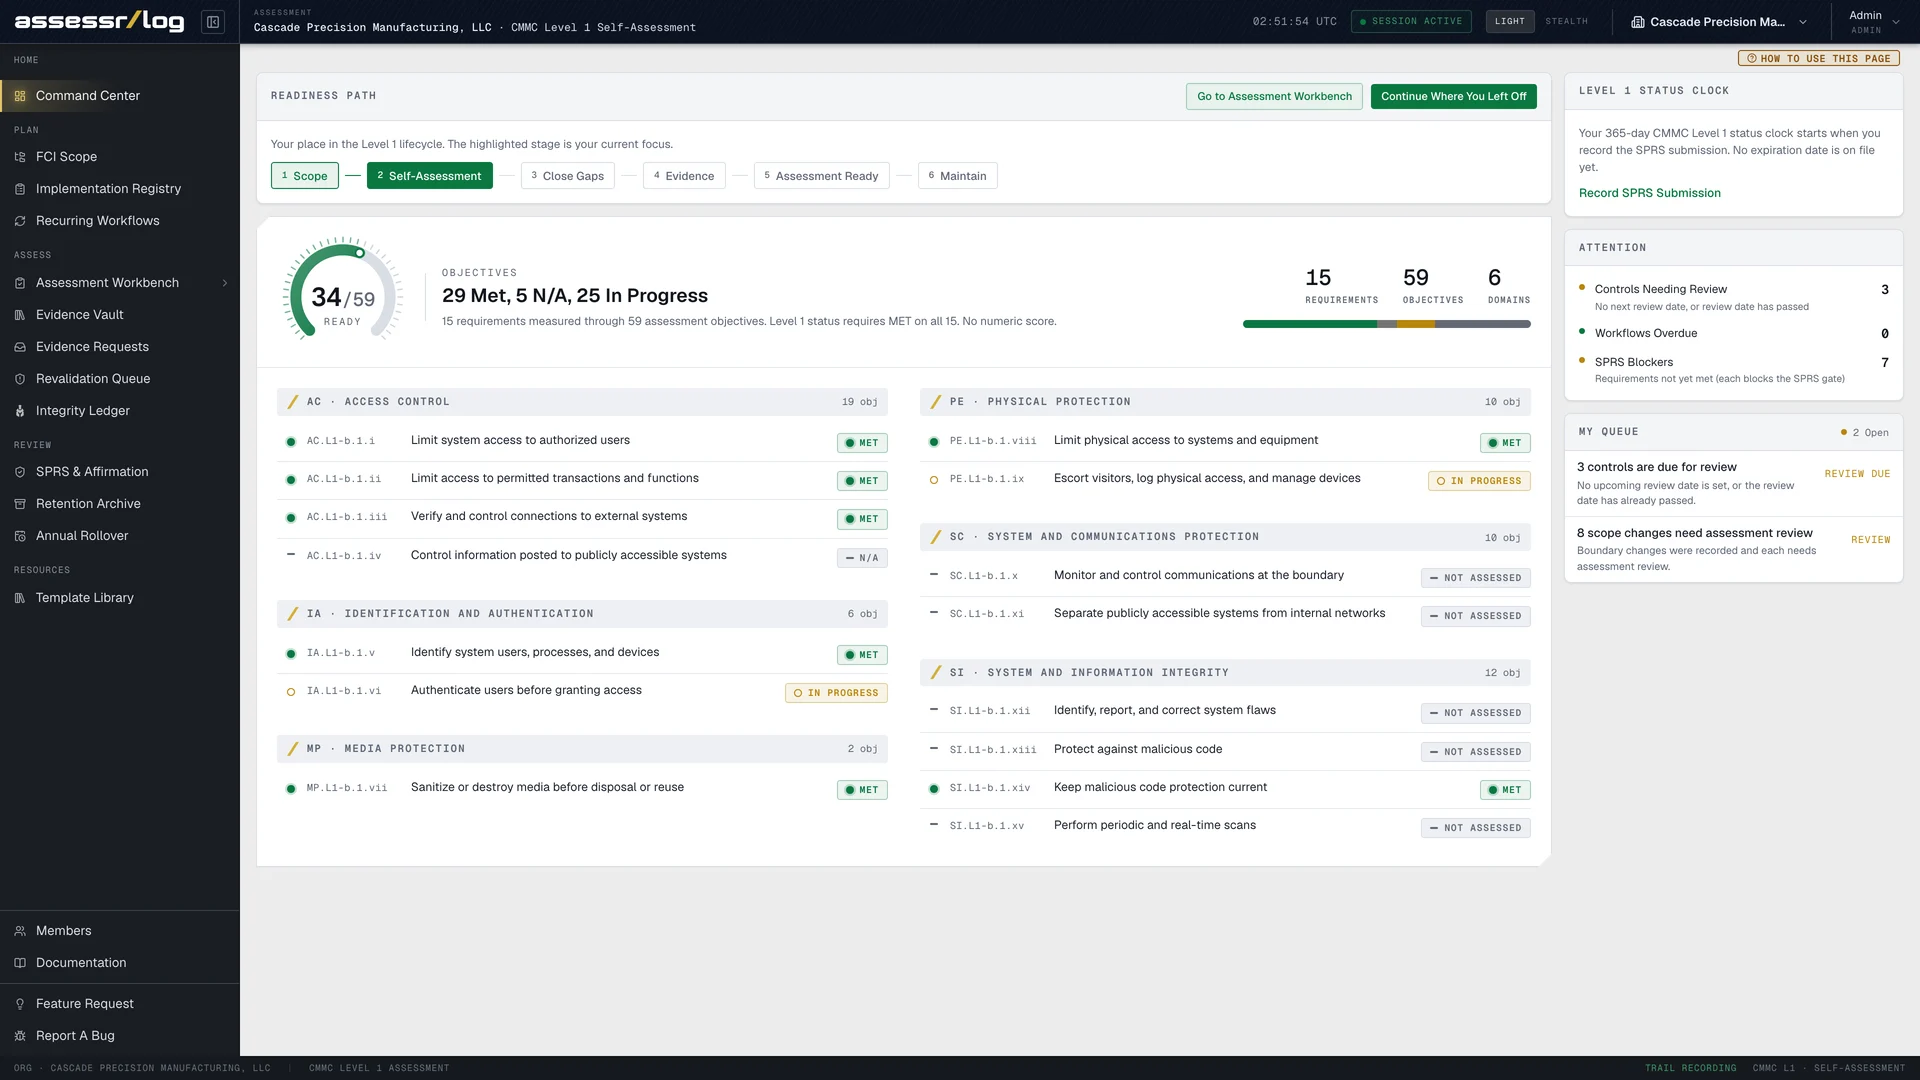
Each requirement breaks into smaller assessment objectives, which come from NIST SP 800-171A (June 2018), the edition 32 CFR 170.15(c)(1)(i) names. There are 59 of them, and they group into six domains. The counts are exact.
- Access Control: 19 objectives
- Identification and Authentication: 6 objectives
- Media Protection: 2 objectives
- Physical Protection: 10 objectives
- System and Communications Protection: 10 objectives
- System and Information Integrity: 12 objectives
Those add to 59. Counts of 49 or 61 match neither DoD guide. The current Version 2.13 guide and the superseded Version 2.0 guide both total 59 objectives. The number is 59, and it is the level of detail you actually assess against.
What CMMC Level 1 Does Not Have
Getting the count right also means getting rid of three things that belong to other levels.
- No numeric score. 32 CFR 170.24(c)(1) says Level 1 self-assessment results "are scored as MET or NOT MET in their entirety." There is no percentage or points total. Every objective must be MET or N/A before you affirm. Anyone showing you a Level 1 "readiness score" is showing you a number the rule does not use.
- No Plan of Action and Milestones. 32 CFR 170.21(a)(1) does not permit one at Level 1. You cannot affirm Level 1 with open items to fix later. Every objective has to be resolved first.
- No certification. Level 1 is a self-assessment, not a certification. No third party certifies you. You assess, you enter the results in SPRS, and a senior official affirms them.
Built Around These Exact Numbers
AssessrLog is built around exactly these numbers. It scopes your Federal Contract Information, walks all 59 objectives across the 15 requirements, and logs each determination as MET, NOT MET, or N/A with its evidence attached. No invented score, no plan-of-action fiction, just the real structure of Level 1 kept in one place. You can see that structure on the product overview.
Frequently Asked Questions
Is CMMC Level 1 15 or 17 controls? It is 15 requirements, from FAR 52.204-21(b)(1), lettered i through xv. The CMMC rule maps them to 17 NIST SP 800-171 numbers because one requirement splits into three. A superseded December 2021 DoD guide also listed 17 practices. The current count is 15.
How many assessment objectives are in Level 1? 59, across six domains, from NIST SP 800-171A (June 2018). The current and the superseded DoD Level 1 guides both total 59. Not 49 and not 61.
Is there a CMMC Level 1 score? There is no numeric score. Results are scored MET or NOT MET in their entirety under 32 CFR 170.24(c)(1). Every objective must be MET or N/A before you affirm, and there is no percentage or points total.
Are they called controls or requirements? FAR 52.204-21(b)(1) introduces them with the phrase security controls. 32 CFR 170.14(c)(2) calls them security requirements, which is the term we use. Level 1 has 15 requirements, broken into 59 objectives.
What is Level 1 protecting? Federal Contract Information, or FCI. The more sensitive Controlled Unclassified Information belongs to Level 2, which is a different and heavier standard.
Primary Sources
Related Reference Pages
Cite This Page
Chris Burkhardt. “CMMC Level 1 Has 15 Requirements, Not 17 Controls.” AssessrLog, a product of ProfytAI Pte. Ltd.. Updated October 3, 2026. https://assessrlog.com/blog/cmmc-level-1-requirements-15-not-17/