Built by People Who
Know the Work.
Assessment expertise. Platform engineering. AssessrLog brings both together to turn complex federal assessments into a structured, defensible platform built to scale.
Two Disciplines · One Platform
One Platform for Every Assessment.
Any organization or institution seeking federal funding, a grant, or a government contract has to prove it meets a strict set of requirements. That proof is an assessment.
AssessrLog is the platform where the assessment is carried out and the defensible record behind it is preserved. It starts with CMMC and is built to run every assessment that comes after.
Frameworks In
Assessments come from across defense, higher education, healthcare, and the service providers that support them.
One Working Environment
Requirements, evidence, decisions, and progress are worked in a single, secure environment built for assessment work.
Defensible Record Out
Every result is backed by its evidence and reasoning, and preserved for audit, oversight, and the years to come.
- Defense (CMMC)In Use
- Higher Education
- Healthcare
- Managed Providers
 Engine
- Requirements
- Evidence
- Decisions
- Progress
- Requirements Completed
- Evidence Attached
- Decisions Recorded
- History Preserved
No Assessment on Record.
No Contract on the Table.
Federal funding and contracts come with a condition. Any organization or institution that wants a government contract, a grant, or federal funding has to prove it meets a strict set of security and compliance requirements. That proof is a formal assessment, recorded and affirmed. It reaches across the entire federal supply chain, from prime contractors to the universities, hospitals, and service providers beneath them.
Required to Compete.
Without proof that the requirements are met, the funding or the contract is off the table. Across these programs, the assessment is the gate to the award.
Repeated, Not One and Done.
An assessment is rarely a one-time checkbox. Each program sets its own schedule for proving the work again, and the obligation returns on that cadence.
Owned by a Named Person.
A real person stands behind the result. Whatever the program, the proof has to be true, and the accountability for it outlives the assessment itself.
The Auditors Are Gone.
The Requirement Remains.
Federal cybersecurity just shifted. Third-party certification was suspended for a wide band of contractors, while covered defense suppliers stay fully responsible for proving their own security. That moves the weight onto self-assessment, and onto the record that stands behind it. The tooling to run that assessment well did not exist. That is the opening.
Before
Third-Party Certification
A separate body was expected to certify contractors, on a timeline and at a cost that never fit the smaller supplier.
Now
Prove It Yourself, On the Record
Covered suppliers assess and affirm their own security. The proof, and the accountability for it, sits with the company.
A false affirmation is a legal act. Under the False Claims Act it can carry financial and personal liability, so the record has to hold up.
CMMC Is the Wedge.
Assessments Are the Market.
The same engine that runs a CMMC assessment runs the next one. Every framework we take on becomes a new market, and the managed providers who serve many clients multiply the reach. CMMC is where we start, not where we stop.
Defense
Cybersecurity assessments, starting with CMMC.
Higher Education
Research security and the rules that fund it.
Healthcare
Federal programs and the assessments they require.
Managed Providers
One relationship, hundreds of assessments.
The People Behind the Platform.
AssessrLog is built by operators who have led security and compliance inside highly regulated environments and shipped products through public-company scale.
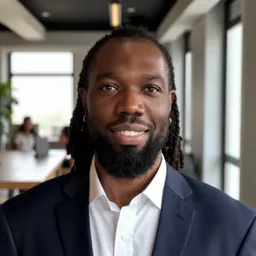
CEO & Co-Founder
Jeff Kangar
Ex-LinkedIn and Deloitte security leader
with 13+ years in GRC.
Background
Ex-LinkedIn and Deloitte cybersecurity leadership. Held a DoD Top Secret clearance, trusted with national security data.
Education
Bachelor of Science, Information Technology.
Regulated Environments
Leads GRC programs in highly regulated environments with national-security-grade trust requirements.
Enterprise Security
Scaled enterprise security programs across cloud and corporate systems at LinkedIn and Deloitte.
Leadership & Strategy
Drives security strategy, risk reduction, and compliance execution across complex organizations.
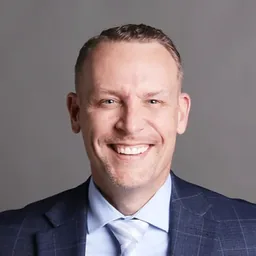
CTO & Co-Founder
Chris Burkhardt
Founder-Operator with 20+ years building products across industries.
Background
Founding Engineer at TrueCar (NASDAQ IPO). Principal Engineer at Beachbody (NYSE IPO). Principal AI Engineer at Asurion.
Education
Master of Engineering, AI & Cybersecurity Cloud Management.
Startup Founding
Built companies from zero to launch as both CEO and CTO across Japan, Vietnam, and the United States.
Public Company Experience
Held Founding Engineer and Principal Engineering roles at TrueCar and Beachbody through IPO-stage growth.
Deep Technical Expertise
Leads AI and cloud architecture, scaling products with distributed engineering teams globally.